How to access OpenSearch Dashboards using OAuth
This guide shows how to configure OpenSearch Dashboards to support single sign-on (SSO) using the Canonical Identity Platform. The platform is a Charm bundle that includes an identity provider (Hydra), an identity broker (Kratos), an ingress (Traefik), and a login-ui application. By the end, you will be able to sign in to OpenSearch Dashboards with an admin user created in Kratos.
Prerequisites
A deployed charmed OpenSearch cluster on LXD.
A deployed charmed OpenSearch Dashboards on LXD and integrated with OpenSearch. See: Deploy, connect, and scale.
A deployed Canonical Identity Platform on Kubernetes.
Working Integration between OpenSearch and Canonical Identity Platform through certificates and Hydra OAuth interface. See: How to access OpenSearch using OAuth.
Note
This guide assumes that LXD and MicroK8s are managed under the same Juju controller
(overlord, as set up in the Tutorial).
Running LXD and MicroK8s under separate controllers may cause failures during
cross-model integration. If you have not yet added MicroK8s to your controller,
add it as follows:
# Export microk8s config
microk8s.kubectl config view --raw > ~/.kube/config

# Replace localhost IP by the computer public IP
export LOCAL_IP="127.0.0.1"
export PUBLIC_IP=$(ip -4 -j route get 2.2.2.2 | jq -r '.[] | .prefsrc')
sed -i 's/'${LOCAL_IP}'/'${PUBLIC_IP}'/g' ~/.kube/config

# Add the microk8s cloud to the existing controller
juju add-k8s microk8s-cluster --controller overlord
After adding the cloud, create a model on it for the Identity Platform:
juju add-model oauth microk8s-cluster
Deploy OpenSearch Dashboards
On the LXD model where OpenSearch is deployed, deploy OpenSearch Dashboards, and integrate it with OpenSearch charm.
juju switch overlord:tutorial
juju deploy opensearch-dashboards --channel=2/edge
juju integrate opensearch opensearch-dashboards
Now, wait for the OpenSearch and OpenSearch Dashboards to become active and ready:
watch juju status
Integrate OpenSearch Dashboards with Canonical Identity Platform
Switch to the oauth model and verify the identity platform bundle is ready:
juju switch overlord:oauth
juju status
Output example
Model  Controller  Cloud/Region                Version  SLA          Timestamp
oauth  overlord    microk8s-cluster/localhost  3.6.10   unsupported  15:38:54Z

App                                  Version  Status   Scale  Charm                                Channel        Rev  Address         Exposed  Message
hydra                                v2.3.0   active       1  hydra                                latest/edge    339  10.152.183.124  no
identity-platform-login-ui-operator  0.21.2   active       1  identity-platform-login-ui-operator  latest/edge    146  10.152.183.25   no
kratos                               v1.3.1   active       1  kratos                               latest/edge    500  10.152.183.20   no
kratos-external-idp-integrator                blocked      1  kratos-external-idp-integrator       latest/edge    245  10.152.183.113  no       Invalid configuration: Missing required configuration 'client_id' for provider 'generic'
postgresql-k8s                       14.15    active       1  postgresql-k8s                       14/stable      495  10.152.183.109  no
self-signed-certificates                      active       1  self-signed-certificates             1/stable  317 10.152.183.250  no
traefik-admin                        v2.11.0  active       1  traefik-k8s                          latest/stable  176  10.241.7.40     no
traefik-public                       v2.11.0  active       1  traefik-k8s                          latest/stable  176  10.241.7.39     no

Unit                                    Workload  Agent  Address      Ports  Message
hydra/0*                                active    idle   10.1.156.80
identity-platform-login-ui-operator/0*  active    idle   10.1.156.81
kratos-external-idp-integrator/0*       blocked   idle   10.1.156.82         Invalid configuration: Missing required configuration 'client_id' for provider 'generic'
kratos/0*                               active    idle   10.1.156.91
postgresql-k8s/0*                       active    idle   10.1.156.89         Primary
self-signed-certificates/0*             active    idle   10.1.156.83
traefik-admin/0*                        active    idle   10.1.156.90
traefik-public/0*                       active    idle   10.1.156.86
All the components of the bundle must be active except kratos-external-idp-integrator.
It is in blocked status.
Before switching back to the LXD model, offer the hydra:oauth and
self-signed-certificates:certificates endpoints from the OAuth model so they
can be consumed cross-model by the OpenSearch Dashboards model:
juju offer hydra:oauth
juju offer self-signed-certificates:certificates
Switch back to the OpenSearch Dashboards model and consume the offers:
juju switch overlord:tutorial
juju consume admin/oauth.hydra
juju consume admin/oauth.self-signed-certificates
Now integrate OpenSearch Dashboards with the consumed offers:
juju integrate opensearch-dashboards:certificates self-signed-certificates:certificates
juju integrate opensearch-dashboards:oauth hydra:oauth
Create an admin account
Create an admin account using Kratos. This command requires an email and username, and prints the password reset link as well as the reset code:
juju run kratos/leader create-admin-account email=myuser@example.com username=myuser --model overlord:oauth
The output is similar to the following:
Running operation 1 with 1 task
  - task 2 on unit-kratos-0

Waiting for task 2...
15:39:52 Creating admin account.
15:39:53 Successfully created admin account: 3b322477-6250-4606-b820-b32d679b3cff.
15:39:53 Creating recovery code for resetting admin password.

expires-at: "2025-09-25T16:39:52.595790816Z"
identity-id: 3b322477-6250-4606-b820-b32d679b3cff
password-reset-code: "868748"
password-reset-link: https://10.241.7.39/welcome-k8s-identity-platform-login-ui-operator/ui/reset_email?flow=a5966798-646b-46e7-ae6f-a466e30323a9
The output provides a password reset link and recovery code. Open the link, enter the recovery code, and set a password.
Make sure to enter the recovery code given in the output of the previous command. Once that is done, you are redirected to the password reset page, where you specify the user’s password.
Once the password is set, you are prompted to configure 2FA (mandatory).
Access OpenSearch Dashboards using Single Sign-On
To access OpenSearch Dashboards, use the IP address on the opensearch-dashboards/0
unit to form the URL: https://<ip-address>:5601.
Once the account is ready, open OpenSearch Dashboards. A Log in with single sign-on button appears.

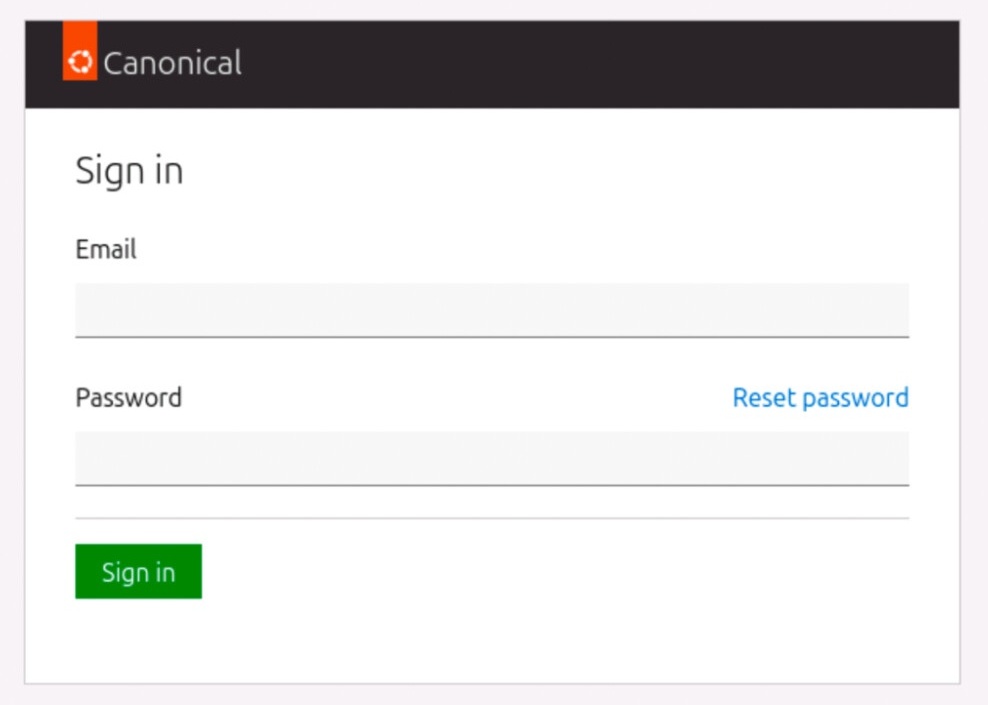
Click the button to open the identity platform login UI. You are redirected to the identity platform UI login screen, where you are prompted to enter the email and password.
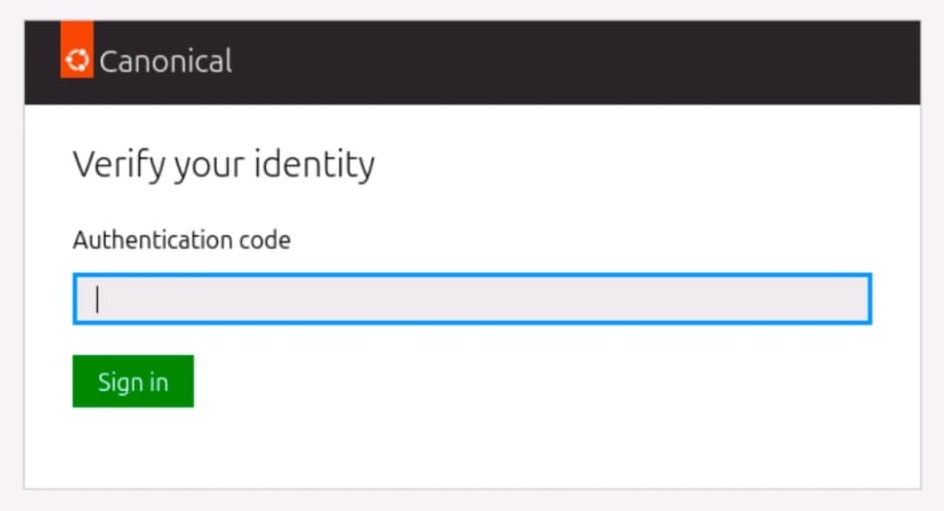
If it is your first time connecting, it also asks for the 2FA code.
After a successful login, you are redirected to the OpenSearch Dashboards home screen.

Next steps
Review the roles mapping section in How to access OpenSearch using OAuth to assign permissions.
Follow the guide How to manage external identity providers to enable logins with providers like GitHub.